Verified capturewww.pixelcity.top
DeepSec,shown working.
A real scan of this website, captured from the local CLI. The output keeps the rule ID, severity, evidence, and remediation together instead of reducing a result to a single pass or fail score.
4
Risk score
Low
3
Web findings
Medium / low / info
0
Source findings
Current web/src scan
01 / Terminal
Findings stay attached to evidence.
deepsec webscan https://www.pixelcity.top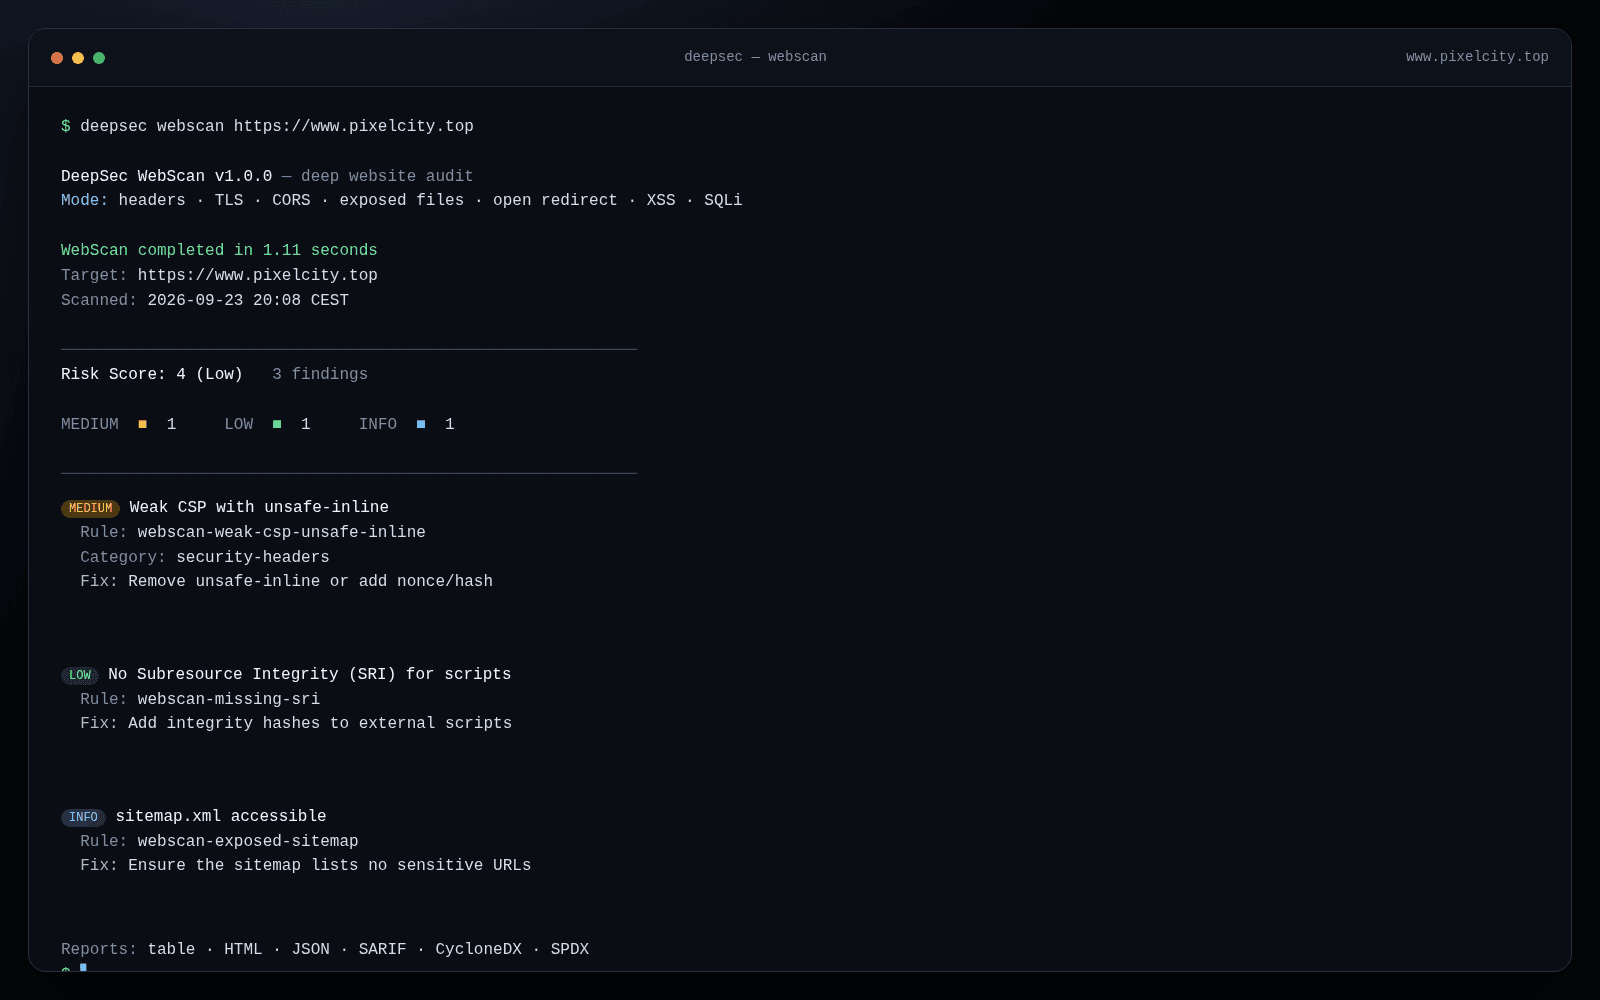
Capture generated on 23 September 2026. The medium CSP and low SRI results are shown as review items; the public sitemap result is informational.
02 / Report
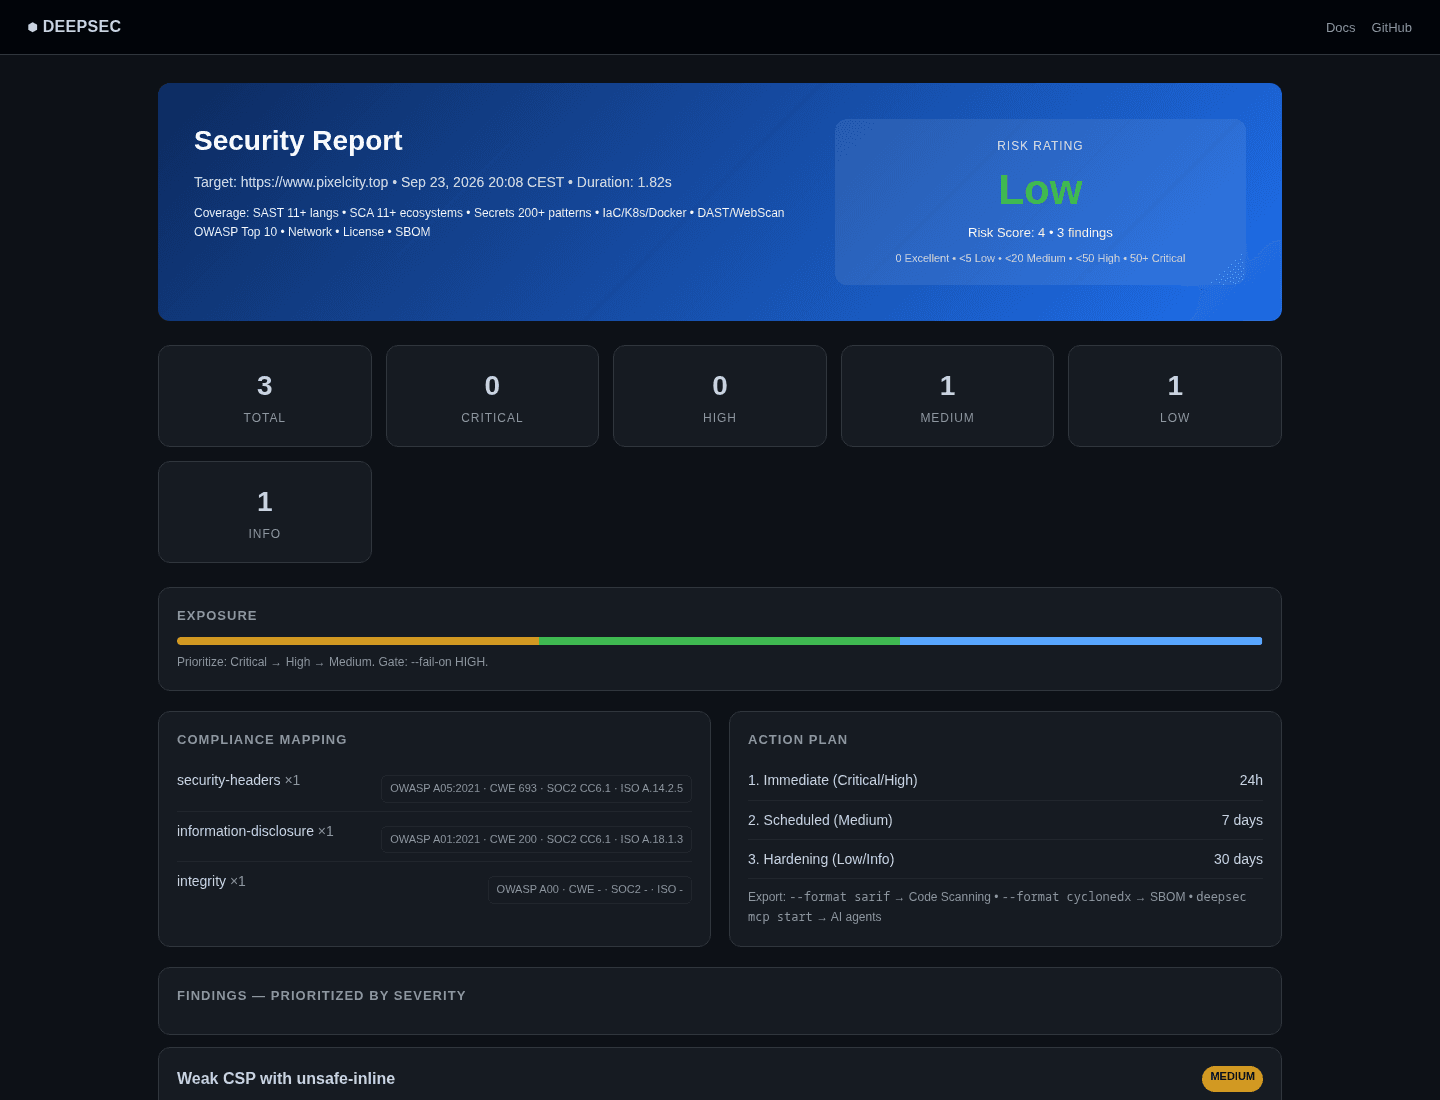
A report built for review.
The HTML report groups the scan by risk, maps rules to OWASP and CWE where available, and prints the remediation text beside each result. The same findings can be exported as SARIF for CI or code scanning.
Table + HTML
Readable review with severity, rule, location, and remediation.
JSON + SARIF
Machine-readable output for CI gates and code-scanning workflows.
CycloneDX + SPDX
Software bill of materials and license inventory exports.
03 / Pipeline
One CLI. Multiple evidence sources.
DeepSec keeps filesystem and HTTP targets in one workflow. Scanner output is normalized before it reaches the report or export stage.
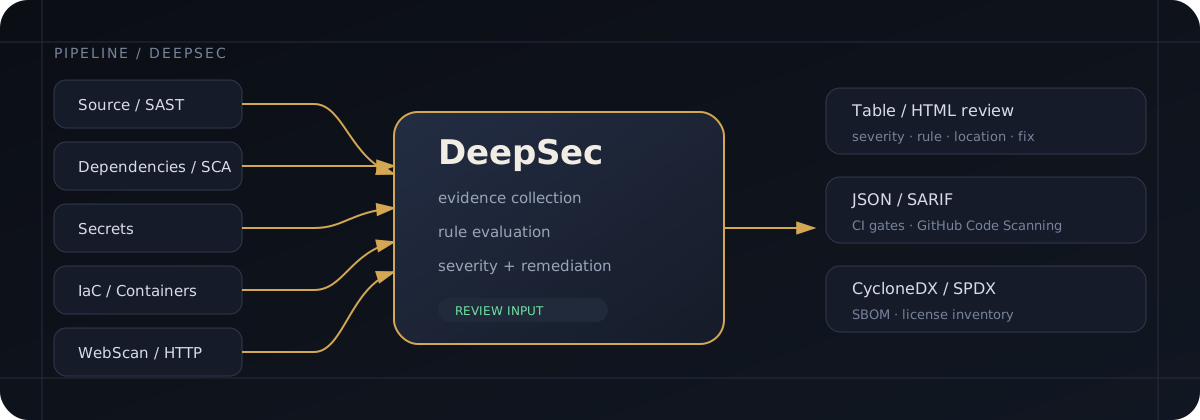
SASTSource patterns
SCADependency risk
SecretsCredential patterns
IaCTerraform and containers
WebScanHTTP configuration
Supply chainSBOM and licenses
Run locally